Picture a 40-person Calgary firm whose network flags unusual traffic at 2 a.m. The system logs the event and sends an alert. Nobody reads it until Monday. That is an intrusion detection system doing exactly what it was built to do, and it is why IDS vs IPS is a business question, not just a technical one.
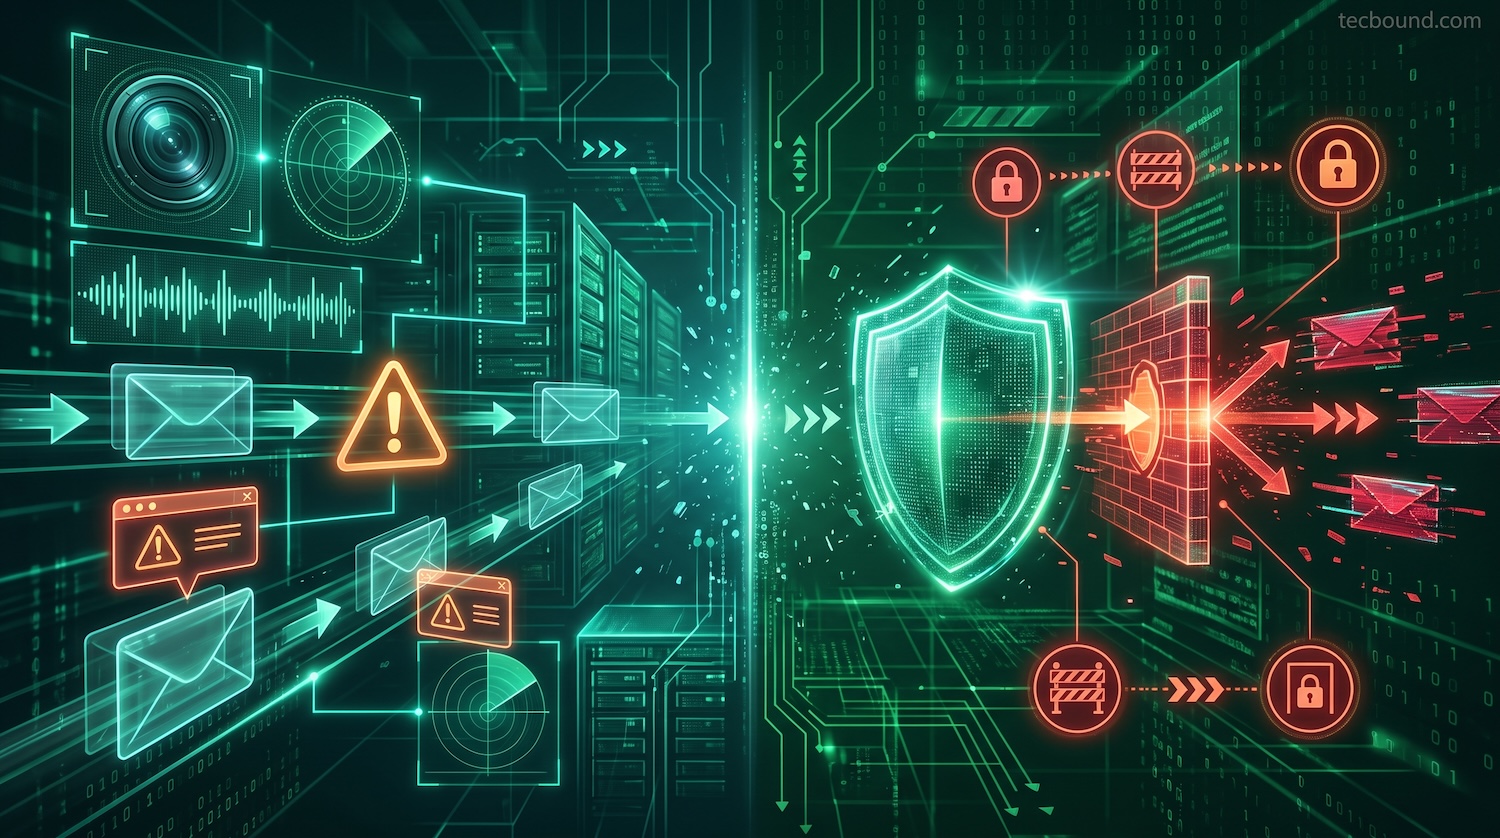
An IDS tells you something is wrong. An IPS can stop it as it happens. Which one your business needs depends on who is watching, how fast you can respond, and how much disruption you can tolerate. This guide explains how each works, how they compare with firewalls, EDR, and XDR, and how to choose the right option for a small or mid-sized business.
An IDS detects suspicious activity and alerts you. An IPS sits in the traffic path and blocks it automatically. Most businesses need both capabilities, usually delivered through a next-generation firewall and endpoint detection rather than separate boxes.
| Factor | IDS | IPS |
|---|---|---|
| Main job | Detect and alert | Detect and block |
| Placement | Out of band, on a copy of traffic | Inline, in the traffic path |
| Response | A person or another tool acts after the alert | Acts automatically, in real time |
| Main risk | Alerts nobody reads, slow response | False positives can block legitimate traffic |
| Best for | Visibility, investigation, compliance logging | Stopping known attacks at the network edge |
An intrusion detection system (IDS) monitors network traffic or system activity for signs of malicious behaviour and policy violations, then alerts your team. It does not block anything on its own. Think of it as a security camera: it records and raises the alarm, but it does not lock the door.
An IDS watches a copy of your traffic, usually fed from a switch’s mirror (SPAN) port or a network TAP, so it never sits in the data path. It compares what it sees against known attack patterns, behavioural baselines, or both. When something matches, it generates an alert and logs the details for investigation.
Because it is passive, an IDS cannot slow down or interrupt your network. It also cannot stop an attack on its own.
A network-based IDS (NIDS) monitors traffic at key points, such as the network perimeter or between internal segments. It sees activity across many devices at once, but it has limited visibility into encrypted traffic unless TLS inspection is in place.
A host-based IDS (HIDS) runs on an individual server or workstation. It watches system logs, file integrity, running processes and configuration changes. It can see activity after traffic has been decrypted, which a NIDS often cannot.
Most mature environments combine both for broader coverage.
Signature-based detection matches activity against a database of known attack patterns. It is accurate and produces few false alarms, but it cannot catch a threat it has never seen.
Anomaly-based detection learns what normal looks like in your environment and flags deviations. It can catch new or unusual attacks, but it needs tuning and tends to generate more false positives.
Hybrid detection uses both approaches. It is the most common setup in modern tools because each method covers the other’s blind spots.
Pros
Cons
Open-source options are widely used. Snort and Suricata are the best-known network IDS engines. Zeek focuses on deep network traffic analysis and logging. Wazuh and OSSEC are common host-based options, and Security Onion bundles several of these tools into one monitoring platform.
These tools are powerful, but they need skilled staff to deploy, tune, and watch. For a smaller team, that is a real cost.
An intrusion prevention system (IPS) does everything an IDS does, then takes action. It sits directly in the path of traffic, inspects it, and can block malicious activity before it reaches its target. If an IDS is the security camera, an IPS is a checkpoint with the authority to turn someone away.
An IPS is deployed inline, so all traffic passes through it. It inspects that traffic using the same signature, anomaly and policy-based methods as an IDS. When it finds a threat, it can drop the offending packets, reset the connection, block the source IP address, or alert your team.
Because it works in real time, an IPS can contain many known attacks in seconds. The trade-off is that it must be tunedsized and sizedtuned carefully, since a misconfigured IPS can interrupt legitimate traffic.
Most small and mid-sized businesses meet NIPS needs with a next-generation firewall and HIPS with endpoint protection.
Pros
Cons
Snort and Suricata can both run in inline mode and act as an IPS. Commercial options are usually built into network security platforms, including Cisco Secure Firewall (formerly Firepower), Palo Alto Networks, Fortinet FortiGate, Check Point, Sophos and Trend Micro TippingPoint.
For most small and mid-sized businesses, IPS arrives as a licensed feature of a next-generation firewall rather than a standalone appliance. Product names and packaging change often, so confirm current capabilities with the vendor or your IT provider.
The core difference is action: an IDS observes and reports, while an IPS observes and acts.
| Factor | IDS | IPS |
|---|---|---|
| Primary function | Detects and alerts | Detects and blocks |
| Network placement | Out of band, on a copy of traffic | Inline, in the traffic path |
| Response | Manual, or through other tools | Automatic, in real time |
| Impact on traffic | None | Can add latency and can block legitimate traffic if misconfigured |
| If the device fails | Network keeps running | Depends on fail-open or fail-closed setup |
| Typical use | Monitoring, investigation, compliance logging | Active defence at the network edge |
| Tuning effort | Moderate, to reduce alert noise | Higher, to avoid false blocks |
| Cost and complexity | Generally lower to deploy | Generally higher, and more sensitive to sizing |
A firewall controls who can connect. IDS and IPS look at what is happening inside the traffic that is allowed through.
| Technology | What it does | Where it works | Acts automatically? |
|---|---|---|---|
| Firewall | Allows or denies traffic based on rules for IP addresses, ports and protocols | Network perimeter and between segments | Yes, per policy |
| IDS | Detects suspicious activity and alerts | Network or host | No |
| IPS | Detects and blocks suspicious activity | Inline on the network, or on a host | Yes |
| IDPS | Combined term for systems that do both detection and prevention | Network or host | Depends on mode |
| NGFW | Firewall plus application awareness and user identity, usually with built-in IPS and TLS inspection | Network perimeter | Yes |
| EDR | Records endpoint activity, detects threats, and lets responders isolate or remediate a device | Laptops, desktops, servers | Partly, depending on policy |
| XDR | Extends EDR by correlating data across endpoints, network, email, cloud and identity | Multiple layers | Partly, depending on policy |
Managed detection and response (MDR) is not a technology on this list. It is a service in which a security team monitors these tools around the clock and responds to what they find.
For most organizations, the answer is both, used in layers. The right balance depends on how much disruption you can tolerate and how quickly someone can respond.
An IDS fits when blocking is risky or when visibility is the priority.
An IPS fits when speed matters more than the risk of an occasional false block.
Detection and prevention solve different problems. Prevention automatically handles the high volume of known threats. Detection catches what prevention misses, such as new techniques or an attacker who is already inside.
In practice, many businesses run an IPS at the perimeter, detection on internal traffic and endpoints, and send everything to a monitored platform, where someone reviews the alerts. Prevention reduces the noise. Detection provides visibility.
Neither works well without a person or a service acting on what they report. No single control stops everything, so the goal is resilience: spot problems quickly and respond quickly.
Deployment decisions matter as much as product choice. A well-tuned basic setup will outperform an expensive one nobody maintains.
Small and mid-sized businesses need the capability, not necessarily separate IDS and IPS products. Most get IPS through the licensed features of a next-generation firewall, and detection through endpoint detection and response (EDR) and Microsoft 365 or cloud security tools.
The harder part is people. An alert at 2 a.m. only matters if someone reads it and acts. Many smaller teams cannot watch alerts around the clock; they turn to managed detection and response or a co-managed model, where an outside team monitors and responds alongside internal IT.
Regulated and public-sector organizations, including municipal agencies, First Nations Police Services, and financial and legal firms, often face stricter expectations for monitoring and documented response. Frameworks such as PCI DSS and a growing number of cyber insurance applications ask about detection and monitoring controls.
A practical starting checklist:
Neither is better in every situation. An IPS delivers faster, automatic protection against known threats, while an IDS provides safer visibility with no risk of blocking legitimate traffic. Most businesses benefit from both, used in layers and backed by someone who reviews the alerts.
No. A traditional firewall allows or blocks traffic based on rules for addresses, ports and protocols. It does not inspect traffic for attack patterns. Many next-generation firewalls include IPS as an added feature, which is why the terms often get mixed up.
Sometimes. Tools such as Snort and Suricata can run in either mode, and many commercial platforms let you switch from detection to prevention. The device must sit inline to block anything. Most teams run in detection mode first, tune out false positives, then turn on blocking.
It can add some latency, because traffic passes through it for inspection. With properly sized hardware and sensible rules, the effect is usually small. Features such as TLS decryption raise the load, so check performance with them enabled before you buy.
They need the protection, though not necessarily as separate products. Most small businesses get IPS through a next-generation firewall and detection through endpoint tools. The key question is who monitors the alerts and responds, especially after hours.
A network-based IDS (NIDS) watches traffic moving across the network. A host-based IDS (HIDS) runs on a single device and watches its files, logs and processes. NIDS gives breadth across many devices, while HIDS gives depth on one, including activity that network tools cannot see in encrypted traffic.
An IDS tells you something is wrong. An IPS can stop it before it spreads. For most businesses, the right answer is layered: prevention at the edge, detection across the network and endpoints, and a team that reviews alerts and acts on them quickly. The technology matters, but response speed matters just as much.
Want to see what this looks like for your business? Our team can walk through your current setup with you and show where the gaps are.
Get A FREE Subscription To Weekly Cybersecurity Tips So Your Company Doesn’t Become The Next Victim.